HackTool.Python.Impacket.RSC

Other:PUP-gen [PUP] (AVAST); Trojan.Agent.FVAM (BITDEFENDER); Python/Impacket.C potentially unsafe application (NOD32)
Windows




マルウェアタイプ:
ハッキングツール
破壊活動の有無:
なし
暗号化:

感染報告の有無 :
はい
概要
プログラムは、他のマルウェアに作成されるか、悪意あるWebサイトからユーザが誤ってダウンロードすることによりコンピュータに侵入します。
プログラムは、ワーム活動の機能を備えていません。
プログラムは、バックドア活動の機能を備えていません。
詳細
侵入方法
プログラムは、他のマルウェアに作成されるか、悪意あるWebサイトからユーザが誤ってダウンロードすることによりコンピュータに侵入します。
感染活動
プログラムは、ワーム活動の機能を備えていません。
バックドア活動
プログラムは、バックドア活動の機能を備えていません。
ルートキット機能
プログラムは、ルートキット機能を備えていません。
情報漏えい
プログラムは、以下の情報を収集します。
- Note that this hacking tool does not have any routine to gather or steal information from the host machine running the script.
- However, when executed against an Active Directory environment, it extracts and steals the following forest-level credentials:
- Child-domain krbtgt account NTLM hashes and Kerberos encryption keys
- Forest root Enterprise Admin account credentials and password hashes
- Security Identifiers (SIDs) of the child domain and parent forest domains
その他
プログラムは、以下を実行します。
- It displays the list of parameters that can be used when executed without parameters in a console:
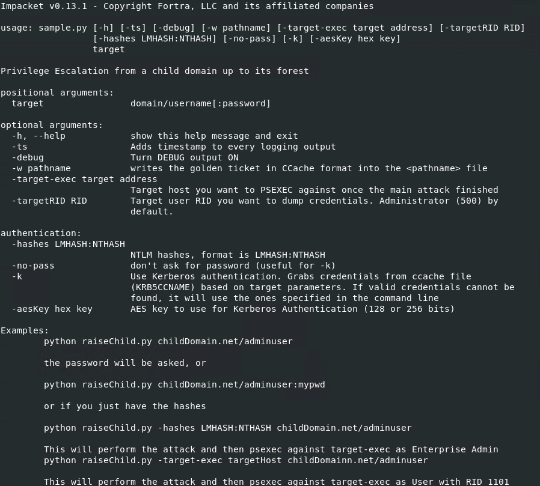
- Operates as an Active Directory domain escalation script within the open-source Impacket framework, utilizing Impacket Kerberos, Netlogon, and DRSUAPI libraries to forge Golden Tickets and achieve forest root administrative access.
- Connects to the child domain controller using Netlogon Remote Protocol ([MS-NRPC]) to discover domain topology and locate the forest root domain FQDN.
- Queries the Local Security Authority ([MS-LSAT]) to resolve and obtain the Enterprise Admins SID of the forest root domain.
- Performs a DCSync attack via Directory Replication Service ([MS-DRSR]) against the child domain controller to dump the child domain's krbtgt account secret key.
- Forges a forged Kerberos Ticket-Granting Ticket (Golden Ticket) in memory, injecting the forest's Enterprise Admin SID into the KERB_VALIDATION_INFO structure's ExtraSids array and configuring a 10-year expiration timestamp.
- Authenticates into the forest root domain controller using the forged ticket to query and retrieve credentials of the forest root Administrator (or specified target RID).
- If the -w parameter is specified: Saves the forged ticket to disk in CCache format for persistence and lateral movement.
- If the -target-exec parameter is specified: Automatically installs a temporary service on the target host over SMB running cmd.exe as SYSTEM or Enterprise Admin, communicating over dedicated named pipes (RemCom_communicaton, RemCom_stdin, RemCom_stdout, RemCom_stderr), supporting interactive shell subcommands (shell, get, put, lcd), and uninstalls the service upon completion.
マルウェアは、以下のパラメータを受け取ります。
- -aesKey {Hex Key} → used to specify an AES key (128 or 256 bits) for Kerberos authentication.
- -dc-ip {IP Address} → used to specify the IP address of the domain controller.
- -debug → used to enable diagnostic debug logging output.
- -hashes {LMHASH:NTHASH} → used to specify NTLM password hashes for Pass-the-Hash authentication.
- -k → used to enable Kerberos authentication using credentials from a Kerberos credential cache file (KRB5CCNAME).
- -no-pass → used to disable password prompting when using Kerberos authentication.
- -target-exec {Target Address} → used to specify the target host to launch a PsExec shell against with Enterprise Admin privileges.
- -targetRID {RID} → used to specify the target user RID to dump credentials for (default: 500 / Administrator).
- -ts → used to prepend timestamps to console logging output.
- -w {File Path} → used to specify the pathname to write the generated Golden Ticket in CCache format.
- target → positional argument specifying child domain administrator credentials in domain/username[:password] format.
マルウェアは、脆弱性を利用した感染活動を行いません。
対応方法
手順 1
Windows 7、Windows 8、Windows 8.1、および Windows 10 のユーザは、コンピュータからマルウェアもしくはアドウェア等を完全に削除するために、ウイルス検索の実行前には必ず「システムの復元」を無効にしてください。
手順 2
最新のバージョン(エンジン、パターンファイル)を導入したウイルス対策製品を用い、ウイルス検索を実行してください。「HackTool.Python.Impacket.RSC」と検出したファイルはすべて削除してください。 検出されたファイルが、弊社ウイルス対策製品により既に駆除、隔離またはファイル削除の処理が実行された場合、ウイルスの処理は完了しており、他の削除手順は特にありません。
ご利用はいかがでしたか? アンケートにご協力ください