Ransom.Win64.ANOBSIDI.THLBBBE

Win64:MalwareX-gen [Ransom] (AVAST)
Windows




Threat Type: Ransomware
Destructiveness: No
Encrypted: No
In the wild: Yes
OVERVIEW
This Ransomware arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
However, as of this writing, the said sites are inaccessible.
It encrypts files found in specific folders. It avoids encrypting files with the following file extensions.
TECHNICAL DETAILS
Arrival Details
This Ransomware arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
Installation
This Ransomware adds the following folders:
- %AppDataLocal%\com.ahadu.pikachu-gamestar
- %AppDataLocal%\com.ahadu.pikachu-gamestar\EBWebView → Contains files for web content
(Note: %AppDataLocal% is the Local Application Data folder, which is usually C:\Documents and Settings\{user name}\Local Settings\Application Data on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\AppData\Local on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).)
It adds the following processes:
- "%Program Files%\Microsoft\EdgeWebView\Application\{version}\msedgewebview2.exe" --embedded-browser-webview=1 --webview-exe-name={malware name}.exe --webview-exe-version={version} --user-data-dir="%AppDataLocal%\com.ahadu.pikachu-gamestar\EBWebView" --noerrdialogs --embedded-browser-webview-dpi-awareness={default} --autoplay-policy=no-user-gesture-required --disable-features={disabled features} --lang=en-US --mojo-named-platform-channel-pipe={mojo handle}
- "%Program Files%\Microsoft\EdgeWebView\Application\{version}\msedgewebview2.exe" --type=crashpad-handler --user-data-dir=%AppDataLocal%\com.ahadu.pikachu-gamestar\EBWebView /prefetch:4 --monitor-self-annotation=ptype=crashpad-handler --database=%AppDataLocal%\com.ahadu.pikachu-gamestar\EBWebView\Crashpad --annotation=IsOfficialBuild=1 --annotation=channel= --annotation=chromium-version={version} "--annotation=exe=%Program Files%\Microsoft\EdgeWebView\Application\{version}\msedgewebview2.exe" --annotation=plat=Win64 "--annotation=prod=Edge WebView2" --annotation=ver={version} --initial-client-data={default}
- "%Program Files%\Microsoft\EdgeWebView\Application\{version}\msedgewebview2.exe" --type=gpu-process --noerrdialogs --user-data-dir="%AppDataLocal%\com.ahadu.pikachu-gamestar\EBWebView" --webview-exe-name={malware name}.exe --webview-exe-version={version} --embedded-browser-webview={default} --embedded-browser-webview-dpi-awareness={default} --no-pre-read-main-dll --gpu-preferences={gpu settings}--startup-read-main-dll --metrics-shmem-handle={default} --field-trial-handle={default} --enable-features={enabled features} --disable-features={disabled features} --variations-seed-version --mojo-platform-channel-handle={mojo handle} /prefetch:2
- "%Program Files%\Microsoft\EdgeWebView\Application\{version}\msedgewebview2.exe" --type=utility --utility-sub-type=network.mojom.NetworkService --lang=en-US --service-sandbox-type=none --noerrdialogs --user-data-dir="%AppDataLocal%\com.ahadu.pikachu-gamestar\EBWebView" --webview-exe-name={malware name}.exe --webview-exe-version={version} --embedded-browser-webview={default} --embedded-browser-webview-dpi-awareness={default} --no-pre-read-main-dll --startup-read-main-dll --metrics-shmem-handle={default} --field-trial-handle={default} --enable-features={enabled features} --disable-features={disabled features} --variations-seed-version --mojo-platform-channel-handle={mojo handle} /prefetch:3
- "%Program Files%\Microsoft\EdgeWebView\Application\{version}\msedgewebview2.exe" --type=utility --utility-sub-type=storage.mojom.StorageService --lang=en-US --service-sandbox-type=service --noerrdialogs --user-data-dir="%AppDataLocal%\com.ahadu.pikachu-gamestar\EBWebView" --webview-exe-name={malware name}.exe --webview-exe-version={version} --embedded-browser-webview={default} --embedded-browser-webview-dpi-awareness={default} --no-pre-read-main-dll --startup-read-main-dll --metrics-shmem-handle={default} --field-trial-handle={default} --enable-features={enabled features} --disable-features={disabled features} --variations-seed-version --mojo-platform-channel-handle={mojo handle} /prefetch:8
- "%Program Files%\Microsoft\EdgeWebView\Application\{version}\msedgewebview2.exe" --type=renderer --noerrdialogs --user-data-dir="%AppDataLocal%\com.ahadu.pikachu-gamestar\EBWebView" --webview-exe-name={malware name}.exe --webview-exe-version={version} --embedded-browser-webview={default} --embedded-browser-webview-dpi-awareness={default} --no-pre-read-main-dll --autoplay-policy=no-user-gesture-required --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=2 --enable-main-frame-before-activation --renderer-client-id=5 --js-flags="--expose-gc --ms-user-locale=" --time-ticks-at-unix-epoch={default} --launch-time-ticks=3758916019 --ssd-no-pressure-read-main-dll --metrics-shmem-handle={default} --field-trial-handle={default} --enable-features={enabled features} --disable-features={disabled features} --variations-seed-version --mojo-platform-channel-handle={mojo handle} /prefetch:1
- "%Program Files%\Microsoft\EdgeWebView\Application\{version}\msedgewebview2.exe" --type=gpu-process --disable-gpu-sandbox --use-gl=disabled --gpu-vendor-id={id} --gpu-device-id={id} --gpu-sub-system-id={id} --gpu-revision=0 --gpu-driver-version={version} --noerrdialogs --user-data-dir="%AppDataLocal%\com.ahadu.pikachu-gamestar\EBWebView" --webview-exe-name={malware name}.exe --webview-exe-version={version} --embedded-browser-webview={default} --embedded-browser-webview-dpi-awareness={default} --no-pre-read-main-dll --gpu-preferences={default} --ssd-no-pressure-read-main-dll --metrics-shmem-handle={default} --field-trial-handle={default} --enable-features={enabled features} --disable-features={disabled features} --variations-seed-version --mojo-platform-channel-handle={mojo handle} /prefetch:8
(Note: %AppDataLocal% is the Local Application Data folder, which is usually C:\Documents and Settings\{user name}\Local Settings\Application Data on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\AppData\Local on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).)
Information Theft
This Ransomware gathers the following data:
- HWID → hardware identification
- Game ID
- Game name
Stolen Information
This Ransomware sends the gathered information via HTTP POST to the following URL:
- https://api.{BLOCKED}.org/bot8590616982:AAExi_dyOLmb_J7FTIr5LZZeAaTs2AOlHPg/sendMessage → telegram bot exfiltration
Other Details
This Ransomware connects to the following possibly malicious URL:
- http://{BLOCKED}.33:3009/api/checkkey
- http://{BLOCKED}.33:3009/api/updateversion
- http://{BLOCKED}.33:3009/api/announcements
- http://{BLOCKED}.33:3009/api/checkremaining
- http://{BLOCKED}.33:3009/api/loginhwid
- http://{BLOCKED}0.r2.dev/GAMEID.zip
- http://{BLOCKED}m.com.tr:3009
It does the following:
- It shows the following GUI with the window title "Pikachu Gamestar" using Microsoft Edge WebView2 to display the ransom note:
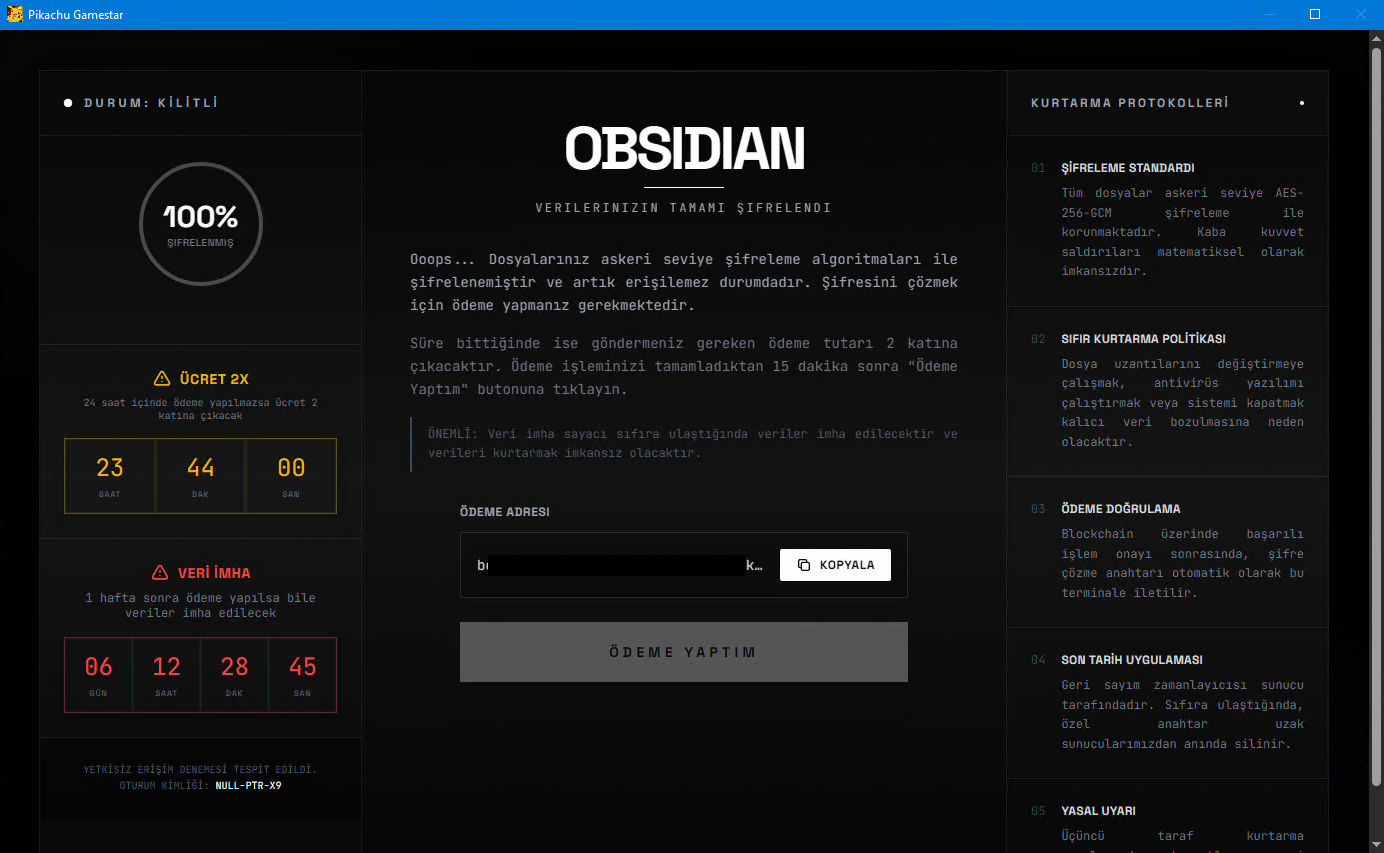
- It uses the following icon to trick users into thinking that it is a legitimate game or software:

However, as of this writing, the said sites are inaccessible.
Ransomware Routine
This Ransomware encrypts files found in the following folders:
- %Desktop%
(Note: %Desktop% is the current user's desktop, which is usually C:\Documents and Settings\{User Name}\Desktop on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\Desktop on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).)
It appends the following extension to the file name of the encrypted files:
- .encrypted
It avoids encrypting files with the following file extensions:
- .encrypted
SOLUTION
Step 1
Before doing any scans, Windows 7, Windows 8, Windows 8.1, and Windows 10 users must disable System Restore to allow full scanning of their computers.
Step 2
Note that not all files, folders, and registry keys and entries are installed on your computer during this malware's/spyware's/grayware's execution. This may be due to incomplete installation or other operating system conditions. If you do not find the same files/folders/registry information, please proceed to the next step.
Step 3
Search and delete this folder
- %AppDataLocal%\com.ahadu.pikachu-gamestar
Step 4
Scan your computer with your Trend Micro product to delete files detected as Ransom.Win64.ANOBSIDI.THLBBBE. If the detected files have already been cleaned, deleted, or quarantined by your Trend Micro product, no further step is required. You may opt to simply delete the quarantined files. Please check the following Trend Micro Support pages for more information:
Step 5
Restore encrypted files from backup.
Did this description help? Tell us how we did.