PUA.Win32.IObit.P

Misleading:Win32/Lodi (MICROSOFT)
Windows



Threat Type: Potentially Unwanted Application
Destructiveness: No
Encrypted: No
In the wild: Yes
OVERVIEW
This Potentially Unwanted Application arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
It does not have any propagation routine.
It does not have any backdoor routine.
It does not have any information-stealing capability.
TECHNICAL DETAILS
Arrival Details
This Potentially Unwanted Application arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
Installation
This Potentially Unwanted Application drops the following files:
- %User Temp%\is-{5 random alphanumeric}.tmp\Setup.exe
- %User Temp%\is-{5 random alphanumeric}.tmp\Installer\Setup.exe
- %User Temp%\is-{5 random alphanumeric}.tmp\libcrypto-1_1.dll
- %User Temp%\is-{5 random alphanumeric}.tmp\Installer\libcrypto-1_1.dll
- %User Temp%\is-{5 random alphanumeric}.tmp\libssl-1_1.dll
- %User Temp%\is-{5 random alphanumeric}.tmp\Installer\libssl-1_1.dll
- %User Temp%\Installerupt45804.5536165393.zlb
- %User Temp%\is-{5 random alphanumeric}.tmp\{malware filename}.tmp
- %Application Data%\IObit\IObit Uninstaller\Installer\2025-05-27.dbg
- %User Temp%\is-{5 random alphanumeric}.tmp\iush.exe
- %User Temp%\is-{5 random alphanumeric}.tmp\Installer\iushrun.exe
- %User Temp%\TempMain.ini
- %User Temp%\filectl.dll
- %ProgramData%\Microsoft\Windows\Start Menu\Programs\IObit Uninstaller\IObit Uninstaller.lnk
- %ProgramData%\Microsoft\Windows\Start Menu\Programs\IObit Uninstaller\Uninstall IObit Uninstaller.lnk
- %Desktop%\IObit Uninstaller.lnk
- %ProgramData%\Microsoft\Windows\Start Menu\Programs\IObit Uninstaller.lnk
- %ProgramData%\ProductData\un11Stat.ini
- %ProgramData%\ProductData\StatCache.db
- %ProgramData%\IObit\IObit Uninstaller\IUService.ini
- %Application Data%\Microsoft\Internet Explorer\Quick Launch\User Pinned\StartMenu\IObit Uninstall Tool.lnk
- %Application Data%\Microsoft\Windows\Templates\Temp.exe
- %Application Data%\Microsoft\Internet Explorer\Quick Launch\User Pinned\StartMenu\Temp.lnk
- %Application Data%\IObit\IObit Uninstaller\MenuRight.dat
- %Application Data%\IObit\IObit Uninstaller\Main.ini
- %Application Data%\IObit\IObit Uninstaller\UninstallHistory.ini
- %Application Data%\IObit\IObit Uninstaller\Log\2025-05-27.dbg
- %ProgramData%\IObit\Install.ini
- %AppDataLocalLow%\IObit\AC.ini
- %ProgramData%\IObit\IObitRtt\IURtt.ept
- %ProgramData%\IObit\iobitpromotion.ini
- %Program Files%\IObit\IObit Uninstaller\CrRestore.exe
- %Program Files%\IObit\IObit Uninstaller\datastate.dll
- %Program Files%\IObit\IObit Uninstaller\DSPut.exe
- %Program Files%\IObit\IObit Uninstaller\Feedback.exe
- %Program Files%\IObit\IObit Uninstaller\filectl.dll
- %Program Files%\IObit\IObit Uninstaller\forcedelctl.dll
- %Program Files%\IObit\IObit Uninstaller\HdProm.dll
- %Program Files%\IObit\IObit Uninstaller\HistoryTemp.txt
- %Program Files%\IObit\IObit Uninstaller\InfoHelp.dll
- %Program Files%\IObit\IObit Uninstaller\installapk.ico
- %Program Files%\IObit\IObit Uninstaller\IObitDownloader.exe
- %Program Files%\IObit\IObit Uninstaller\IObitUninstaler.exe
- %Program Files%\IObit\IObit Uninstaller\IUMenuRight.dll
- %Program Files%\IObit\IObit Uninstaller\IUProtip.exe
- %Program Files%\IObit\IObit Uninstaller\IUService.exe
- %Program Files%\IObit\IObit Uninstaller\iush.exe
- %Program Files%\IObit\IObit Uninstaller\lang.dat
- %Program Files%\IObit\IObit Uninstaller\libcrypto-1_1.dll
- %Program Files%\IObit\IObit Uninstaller\libssl-1_1.dll
- %Program Files%\IObit\IObit Uninstaller\madbasic_.bpl
- %Program Files%\IObit\IObit Uninstaller\maddisAsm_.bpl
- %Program Files%\IObit\IObit Uninstaller\madexcept_.bpl
- %Program Files%\IObit\IObit Uninstaller\NoteIcon.exe
- %Program Files%\IObit\IObit Uninstaller\PluginHelper.dll
- %Program Files%\IObit\IObit Uninstaller\PPUninstaller.exe
- %Program Files%\IObit\IObit Uninstaller\ProductNews2.dll
- %Program Files%\IObit\IObit Uninstaller\ProductStatistics.dll
- %Program Files%\IObit\IObit Uninstaller\RegisterCom.dll
- %Program Files%\IObit\IObit Uninstaller\rgfpctl.dll
- %Program Files%\IObit\IObit Uninstaller\rtl120.bpl
- %Program Files%\IObit\IObit Uninstaller\ScreenShot.exe
- %Program Files%\IObit\IObit Uninstaller\SendBugReportNew.exe
- %Program Files%\IObit\IObit Uninstaller\SpecUTool.exe
- %Program Files%\IObit\IObit Uninstaller\sqlite3.dll
- %Program Files%\IObit\IObit Uninstaller\SysRest.dll
- %Program Files%\IObit\IObit Uninstaller\unins000.dat
- %Program Files%\IObit\IObit Uninstaller\unins000.exe
- %Program Files%\IObit\IObit Uninstaller\unins000.msg
- %Program Files%\IObit\IObit Uninstaller\UninstallExplorer.dll
- %Program Files%\IObit\IObit Uninstaller\UninstallMonitor.exe
- %Program Files%\IObit\IObit Uninstaller\UninstallPromote.exe
- %Program Files%\IObit\IObit Uninstaller\vcl120.bpl
- %Program Files%\IObit\IObit Uninstaller\vclx120.bpl
- %Program Files%\IObit\IObit Uninstaller\webres.dll
- %Program Files%\IObit\IObit Uninstaller\winid.dat
- %Program Files%\IObit\IObit Uninstaller\AUpdate.exe
- %Program Files%\IObit\IObit Uninstaller\AutoUpdate.exe
- %Program Files%\IObit\IObit Uninstaller\BigUpgrade_IU14_13.exe
- %Program Files%\IObit\IObit Uninstaller\Drivers\win7_x86\IUForceDelete.sys
- %Program Files%\IObit\IObit Uninstaller\Drivers\win7_x86\IUProcessFilter.sys
- %Program Files%\IObit\IObit Uninstaller\Drivers\win7_x86\IURegistryFilter.sys
- %Program Files%\IObit\IObit Uninstaller\Drivers\win7_x86\IUFileFilter.sys
(Note: %User Temp% is the current user's Temp folder, which is usually C:\Documents and Settings\{user name}\Local Settings\Temp on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\AppData\Local\Temp on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).. %Application Data% is the current user's Application Data folder, which is usually C:\Documents and Settings\{user name}\Application Data on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\AppData\Roaming on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).. %ProgramData% is a version of the Program Files folder where any user on a multi-user computer can make changes to programs. This contains application data for all users. This is usually C:\ProgramData on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit), or C:\Documents and Settings\All Users on Windows Server 2003(32-bit), 2000(32-bit) and XP.. %Desktop% is the current user's desktop, which is usually C:\Documents and Settings\{User Name}\Desktop on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\Desktop on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).. %AppDataLocalLow% is the LocalLow Application Data folder, which is usually C:\Users\{user name}\AppData\LocalLow on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).. %Program Files% is the default Program Files folder, usually C:\Program Files in Windows 2000(32-bit), Server 2003(32-bit), XP, Vista(64-bit), 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit) , or C:\Program Files (x86) in Windows XP(64-bit), Vista(64-bit), 7(64-bit), 8(64-bit), 8.1(64-bit), 2008(64-bit), 2012(64-bit) and 10(64-bit).)
It adds the following processes:
- %User Temp%\is-{5 random alphanumeric}.tmp\{malware filename}.tmp /SL5="$220440,26620288,139264,{malware full path}.exe"
- %User Temp%\is-{5 random alphanumeric}.tmp\Installer\Setup.exe /setup "{malware full path}.exe" "" "/Ver=12.4.0.4"
- {malware full path}.exe /verysilent /NORESTART /DIR="%Program Files%\IObit\IObit Uninstaller\" /TASKS="desktopicon, " /do /dt ""
- %User Temp%\is-{5 random alphanumeric}.tmp\{malware filename}.tmp /SL5="$110588,26620288,139264,{malware full path}.exe" /verysilent /NORESTART /DIR="%Program Files%\IObit\IObit Uninstaller\" /TASKS="desktopicon, " /do /dt ""
- %User Temp%\is-{5 random alphanumeric}.tmp\Installer\iushrun.exe /ii "%Program Files%\IObit\IObit Uninstaller"
- %Program Files%\IObit\IObit Uninstaller\iush.exe /if "%Program Files%\IObit\IObit Uninstaller" /dt /insur=
- regsvr32.exe /s "%Program Files%\IObit\IObit Uninstaller\IUMenuRight.dll"
- regsvr32.exe /s "%Program Files%\IObit\IObit Uninstaller\UninstallExplorer.dll"
- %Program Files%\IObit\IObit Uninstaller\DSPut.exe /Now /update /W3sidmVyc2lvbiI6IjAuMC4wLjAiLCJzaG93IjowLCJjbGljayI6MCwibGFzdCI6MH1d
- %Program Files%\IObit\IObit Uninstaller\CrRestore.exe /Backup
- %Program Files%\IObit\IObit Uninstaller\UninstallPromote.exe /INSTALL un12
(Note: %User Temp% is the current user's Temp folder, which is usually C:\Documents and Settings\{user name}\Local Settings\Temp on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\AppData\Local\Temp on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).. %Program Files% is the default Program Files folder, usually C:\Program Files in Windows 2000(32-bit), Server 2003(32-bit), XP, Vista(64-bit), 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit) , or C:\Program Files (x86) in Windows XP(64-bit), Vista(64-bit), 7(64-bit), 8(64-bit), 8.1(64-bit), 2008(64-bit), 2012(64-bit) and 10(64-bit).)
It creates the following folders:
- %Program Files%\IObit
- %Program Files%\IObit\IObit Uninstaller
- %Program Files%\IObit\IObit Uninstaller\History
- %Program Files%\IObit\IObit Uninstaller\Language
- %Program Files%\IObit\IObit Uninstaller\Pub
- %Program Files%\IObit\IObit Uninstaller\Skin
- %Program Files%\IObit\IObit Uninstaller\TaskbarPin
- %Program Files%\IObit\IObit Uninstaller\update
(Note: %Program Files% is the default Program Files folder, usually C:\Program Files in Windows 2000(32-bit), Server 2003(32-bit), XP, Vista(64-bit), 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit) , or C:\Program Files (x86) in Windows XP(64-bit), Vista(64-bit), 7(64-bit), 8(64-bit), 8.1(64-bit), 2008(64-bit), 2012(64-bit) and 10(64-bit).)
Autostart Technique
This Potentially Unwanted Application starts the following services:
- Name: IUProcessFilter
Binary Path: \??\%Program Files%\IObit\IObit Uninstaller\drivers\win7_x86\IUProcessFilter.sys
(Note: %Program Files% is the default Program Files folder, usually C:\Program Files in Windows 2000(32-bit), Server 2003(32-bit), XP, Vista(64-bit), 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit) , or C:\Program Files (x86) in Windows XP(64-bit), Vista(64-bit), 7(64-bit), 8(64-bit), 8.1(64-bit), 2008(64-bit), 2012(64-bit) and 10(64-bit).)
Other System Modifications
This Potentially Unwanted Application adds the following registry entries:
HKEY_LOCAL_MACHINE\SOFTWARE\IObit\
Uninstaller
insur = other
HKEY_LOCAL_MACHINE\SOFTWARE\IObit\
Uninstaller
RttData = {random alphanumeric}
HKEY_LOCAL_MACHINE\SOFTWARE\IObit\
Uninstaller
SID1 = {sid}
HKEY_LOCAL_MACHINE\SOFTWARE\IObit\
Uninstaller
Status = 1
HKEY_LOCAL_MACHINE\SOFTWARE\IObit\
Uninstaller
VerStatus = 1
Propagation
This Potentially Unwanted Application does not have any propagation routine.
Backdoor Routine
This Potentially Unwanted Application does not have any backdoor routine.
Rootkit Capabilities
This Potentially Unwanted Application does not have rootkit capabilities.
Download Routine
This Potentially Unwanted Application downloads the file from the following URL and renames the file when stored in the affected system:
- %Temporary Internet Files%\Content.IE5\7KZJEKTK\active_month[1].php
(Note: %Temporary Internet Files% is the Temporary Internet Files folder, which is usually C:\Documents and Settings\{user name}\Local Settings\Temporary Internet Files on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\AppData\Local\Microsoft\Windows\Temporary Internet Files on Windows Vista, 7 and 2008(64-bit), or C:\Users\{user name}\AppData\Local\Microsoft\Windows\INetCache on Windows 8, 8.1, 2012(64-bit) and 10(64-bit).)
It connects to the following URL(s) to download its component file(s):
- http://{BLOCKED}obit.com/active_month.php?app=un12&pr=iobit&ver=12.4.0.4&uid=3287E5103AEF450B8F9B9345B57685F7&type=1&actv=0&ln=en-US&os=61&user=1&insur=other
- {BLOCKED}ts.iobit.com
Information Theft
This Potentially Unwanted Application does not have any information-stealing capability.
Other Details
This Potentially Unwanted Application adds the following registry keys:
HKEY_LOCAL_MACHINE\SOFTWARE\IObit
HKEY_LOCAL_MACHINE\SOFTWARE\IObit\
Uninstaller
It does the following:
- It is capable of uninstalling applications.
- It displays the following GUI:
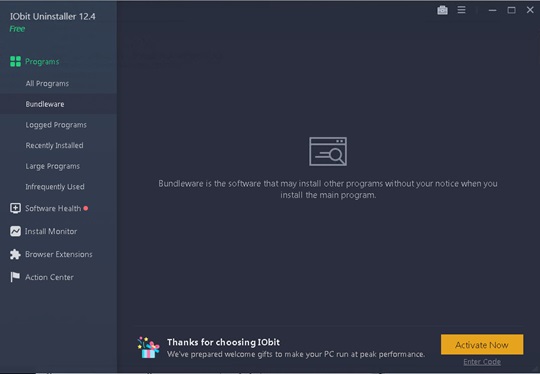
NOTES:
It does not exploit any vulnerability.
SOLUTION
Step 1
Before doing any scans, Windows 7, Windows 8, Windows 8.1, and Windows 10 users must disable System Restore to allow full scanning of their computers.
Step 2
Note that not all files, folders, and registry keys and entries are installed on your computer during this malware's/spyware's/grayware's execution. This may be due to incomplete installation or other operating system conditions. If you do not find the same files/folders/registry information, please proceed to the next step.
Step 3
Search and delete this file
- %User Temp%\is-{5 random alphanumeric}.tmp\Setup.exe
- %User Temp%\is-{5 random alphanumeric}.tmp\Installer\Setup.exe
- %User Temp%\is-{5 random alphanumeric}.tmp\libcrypto-1_1.dll
- %User Temp%\is-{5 random alphanumeric}.tmp\Installer\libcrypto-1_1.dll
- %User Temp%\is-{5 random alphanumeric}.tmp\libssl-1_1.dll
- %User Temp%\is-{5 random alphanumeric}.tmp\Installer\libssl-1_1.dll
- %User Temp%\Installerupt45804.5536165393.zlb
- %User Temp%\is-{5 random alphanumeric}.tmp\{malware filename}.tmp
- %Application Data%\IObit\IObit Uninstaller\Installer\2025-05-27.dbg
- %User Temp%\is-{5 random alphanumeric}.tmp\iush.exe
- %User Temp%\is-{5 random alphanumeric}.tmp\Installer\iushrun.exe
- %User Temp%\TempMain.ini
- %User Temp%\filectl.dll
- %ProgramData%\Microsoft\Windows\Start Menu\Programs\IObit Uninstaller\IObit Uninstaller.lnk
- %ProgramData%\Microsoft\Windows\Start Menu\Programs\IObit Uninstaller\Uninstall IObit Uninstaller.lnk
- %Desktop%\IObit Uninstaller.lnk
- %ProgramData%\Microsoft\Windows\Start Menu\Programs\IObit Uninstaller.lnk
- %ProgramData%\ProductData\un11Stat.ini
- %ProgramData%\ProductData\StatCache.db
- %ProgramData%\IObit\IObit Uninstaller\IUService.ini
- %Application Data%\Microsoft\Internet Explorer\Quick Launch\User Pinned\StartMenu\IObit Uninstall Tool.lnk
- %Application Data%\Microsoft\Windows\Templates\Temp.exe
- %Application Data%\Microsoft\Internet Explorer\Quick Launch\User Pinned\StartMenu\Temp.lnk
- %Application Data%\IObit\IObit Uninstaller\MenuRight.dat
- %Application Data%\IObit\IObit Uninstaller\Main.ini
- %Application Data%\IObit\IObit Uninstaller\UninstallHistory.ini
- %Application Data%\IObit\IObit Uninstaller\Log\2025-05-27.dbg
- %ProgramData%\IObit\Install.ini
- %AppDataLocalLow%\IObit\AC.ini
- %ProgramData%\IObit\IObitRtt\IURtt.ept
- %ProgramData%\IObit\iobitpromotion.ini
- %Program Files%\IObit\IObit Uninstaller\CrRestore.exe
- %Program Files%\IObit\IObit Uninstaller\datastate.dll
- %Program Files%\IObit\IObit Uninstaller\DSPut.exe
- %Program Files%\IObit\IObit Uninstaller\Feedback.exe
- %Program Files%\IObit\IObit Uninstaller\filectl.dll
- %Program Files%\IObit\IObit Uninstaller\forcedelctl.dll
- %Program Files%\IObit\IObit Uninstaller\HdProm.dll
- %Program Files%\IObit\IObit Uninstaller\HistoryTemp.txt
- %Program Files%\IObit\IObit Uninstaller\InfoHelp.dll
- %Program Files%\IObit\IObit Uninstaller\installapk.ico
- %Program Files%\IObit\IObit Uninstaller\IObitDownloader.exe
- %Program Files%\IObit\IObit Uninstaller\IObitUninstaler.exe
- %Program Files%\IObit\IObit Uninstaller\IUMenuRight.dll
- %Program Files%\IObit\IObit Uninstaller\IUProtip.exe
- %Program Files%\IObit\IObit Uninstaller\IUService.exe
- %Program Files%\IObit\IObit Uninstaller\iush.exe
- %Program Files%\IObit\IObit Uninstaller\lang.dat
- %Program Files%\IObit\IObit Uninstaller\libcrypto-1_1.dll
- %Program Files%\IObit\IObit Uninstaller\libssl-1_1.dll
- %Program Files%\IObit\IObit Uninstaller\madbasic_.bpl
- %Program Files%\IObit\IObit Uninstaller\maddisAsm_.bpl
- %Program Files%\IObit\IObit Uninstaller\madexcept_.bpl
- %Program Files%\IObit\IObit Uninstaller\NoteIcon.exe
- %Program Files%\IObit\IObit Uninstaller\PluginHelper.dll
- %Program Files%\IObit\IObit Uninstaller\PPUninstaller.exe
- %Program Files%\IObit\IObit Uninstaller\ProductNews2.dll
- %Program Files%\IObit\IObit Uninstaller\ProductStatistics.dll
- %Program Files%\IObit\IObit Uninstaller\RegisterCom.dll
- %Program Files%\IObit\IObit Uninstaller\rgfpctl.dll
- %Program Files%\IObit\IObit Uninstaller\rtl120.bpl
- %Program Files%\IObit\IObit Uninstaller\ScreenShot.exe
- %Program Files%\IObit\IObit Uninstaller\SendBugReportNew.exe
- %Program Files%\IObit\IObit Uninstaller\SpecUTool.exe
- %Program Files%\IObit\IObit Uninstaller\sqlite3.dll
- %Program Files%\IObit\IObit Uninstaller\SysRest.dll
- %Program Files%\IObit\IObit Uninstaller\unins000.dat
- %Program Files%\IObit\IObit Uninstaller\unins000.exe
- %Program Files%\IObit\IObit Uninstaller\unins000.msg
- %Program Files%\IObit\IObit Uninstaller\UninstallExplorer.dll
- %Program Files%\IObit\IObit Uninstaller\UninstallMonitor.exe
- %Program Files%\IObit\IObit Uninstaller\UninstallPromote.exe
- %Program Files%\IObit\IObit Uninstaller\vcl120.bpl
- %Program Files%\IObit\IObit Uninstaller\vclx120.bpl
- %Program Files%\IObit\IObit Uninstaller\webres.dll
- %Program Files%\IObit\IObit Uninstaller\winid.dat
- %Program Files%\IObit\IObit Uninstaller\AUpdate.exe
- %Program Files%\IObit\IObit Uninstaller\AutoUpdate.exe
- %Program Files%\IObit\IObit Uninstaller\BigUpgrade_IU14_13.exe
- %Program Files%\IObit\IObit Uninstaller\Drivers\win7_x86\IUForceDelete.sys
- %Program Files%\IObit\IObit Uninstaller\Drivers\win7_x86\IUProcessFilter.sys
- %Program Files%\IObit\IObit Uninstaller\Drivers\win7_x86\IURegistryFilter.sys
- %Program Files%\IObit\IObit Uninstaller\Drivers\win7_x86\IUFileFilter.sys
Step 4
Search and delete these folders
- %Program Files%\IObit
- %Program Files%\IObit\IObit Uninstaller
- %Program Files%\IObit\IObit Uninstaller\History
- %Program Files%\IObit\IObit Uninstaller\Language
- %Program Files%\IObit\IObit Uninstaller\Pub
- %Program Files%\IObit\IObit Uninstaller\Skin
- %Program Files%\IObit\IObit Uninstaller\TaskbarPin
- %Program Files%\IObit\IObit Uninstaller\update
Step 5
Delete this registry key
Important: Editing the Windows Registry incorrectly can lead to irreversible system malfunction. Please do this step only if you know how or you can ask assistance from your system administrator. Else, check this Microsoft article first before modifying your computer's registry.
- In HKEY_LOCAL_MACHINE\SOFTWARE\IObit
- In HKEY_LOCAL_MACHINE\SOFTWARE\IObit\Uninstaller
Step 6
Scan your computer with your Trend Micro product to delete files detected as PUA.Win32.IObit.P. If the detected files have already been cleaned, deleted, or quarantined by your Trend Micro product, no further step is required. You may opt to simply delete the quarantined files. Please check the following Trend Micro Support pages for more information:
Did this description help? Tell us how we did.