Trojan.Win64.SPYBOY.A

Windows




Threat Type: Trojan
Destructiveness: No
Encrypted: Yes
In the wild: Yes
OVERVIEW
This Trojan arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
TECHNICAL DETAILS
Arrival Details
This Trojan arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
Installation
This Trojan drops the following files:
- %System%\drivers\{Random Driver Name}.sys - legitimate signed Zemana Anti-Malware driver used to terminate anti-virus processes
(Note: %System% is the Windows system folder, where it usually is C:\Windows\System32 on all Windows operating system versions.)
Other System Modifications
This Trojan adds the following registry entries as part of its installation routine:
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\
Services
{Random Driver Name} = \%System%\drivers\{Random Driver Name}.sys
Process Termination
This Trojan terminates the following processes if found running in the affected system's memory:
- 360rp.exe
- 360rps.exe
- 360Safe.exe
- 360sd.exe
- 360Tray.exe
- 360tray.exe
- Aliyun_assist_service.exe
- AliYunDun.exe
- AliYunDunUpdate.exe
- alsvc.exe
- AmSvc.exe
- aswtoolssvc.exe
- AutoExclusions.exe
- avast!Antivirus.exe
- avastsvc.exe
- avastui.exe
- AvastVBoxSVC.exe
- avgcsrva.exe
- avgidsagent.exe
- avgserv.exe
- AVGSvc.exe
- avgtray.exe
- AVGUI.exe
- avgwdsvca.exe
- AvLaunch.exe
- avp.exe
- avpsus.exe
- avpui.exe
- bccavsvc.exe
- bdagent.exe
- bdmcon.exe
- bdntwrk.exe
- bdoesrv.exe
- bdredline.exe
- bdswitch.exe
- bdwtxcr.exe
- bspatch.exe
- ccsvchst.exe
- coreframeworkhost.exe
- cpda.exe
- cptraylogic.exe
- cptrayui.exe
- CrAmTray.exe
- CrsSvc.exe
- CSFalconContainer.exe
- CSFalconService.exe
- cylancesvc.exe
- CylanceUI.exe
- cyserver.exe
- cytray.exe
- dbserver.exe
- EFRService.exe
- ekrn.exe
- endpoint agent tray.exe
- epab_svc.exe
- epam_svc.exe
- ERAAgent.exe
- ExecutionPreventionSvc.exe
- hmpalert.exe
- idafserverhostservice.exe
- kavfs.exe
- kavfswh.exe
- kavfswp.exe
- klnagent.exe
- ksnproxy.exe
- livesrv.exe
- macmnsvc.exe
- macompatsvc.exe
- masvc.exe
- MBAMService.exe
- MBCloudEA.exe
- McsAgent.exe
- mcsagent.exe
- McsClient.exe
- mcsclient.exe
- mctray.exe
- mfeann.exe
- mfemactl.exe
- mfemms.exe
- minionhost.exe
- mofcomp.exe
- MpCmdRun.exe
- msmpeng.exe
- NisSrv.exe
- Nnx.exe
- Ntrtscan.exe
- paui.exe
- PAV2WSC.exe
- Pccnt.exe
- PccNtMon.exe
- productagentservice.exe
- ProtectedSvc.exe
- PSANCU.exe
- PSINanoRun.exe
- PSNCSysAction.exe
- PSUAMain.exe
- psuaservice.exe
- PSUNMain.exe
- pwd.exe
- PylumLoader.exe
- repmgr.exe
- RepMgr64.exe
- RepUtils.exe
- RepUtils32.exe
- RepUx.exe
- RepWSC64.exe
- SAVAdminService.exe
- SavService.exe
- SBAMSvc.exe
- SBAMTray.exe
- scanhost.exe
- seccenter.exe
- SecurityHealthSystray.exe
- SEDService.exe
- sentinelagent.exe
- SentinelAgentWorker.exe
- sentinelhelperservice.exe
- sentinelservicehost.exe
- sentinelstaticenginescanner.exe
- SentinelUI.exe
- sepagent.exe
- sepWscSvc64.exe
- Sophos UI.exe
- SophosFileScanner.exe
- SophosFIMService.exe
- SophosFS.exe
- SophosHealth.exe
- SophosNetFilter.exe
- SophosNtpService.exe
- SophosSafestore.exe
- SophosUI.exe
- SpySweeperUI.exe
- SSPService.exe
- svcGenericHost.exe
- tlaworker.exe
- TMBMSRV.exe
- TmCCSF.exe
- TmListen.exe
- TmProxy.exe
- TopsecClient.exe
- TopsecDaemon.exe
- TopsecMain.exe
- TopsecTray.exe
- Topsecusysdiag.exe
- updaterui.exe
- updatesrv.exe
- vapm.exe
- VipreAAPSvc.exe
- VipreEdgeProtection.exe
- VipreNis.exe
- vsserv.exe
- vsservp.exe
- vstskmgr.exe
- WAScanner.exe
- WRConsumerService.exe
- WRCoreService.x64.exe
- wrsa.exe
- WRSkyClient.x64.exe
- WscIfSvc.exe
- wscommunicator.exe
- xcommsvr.exe
Other Details
This Trojan does the following:
- It displays the following upon execution:
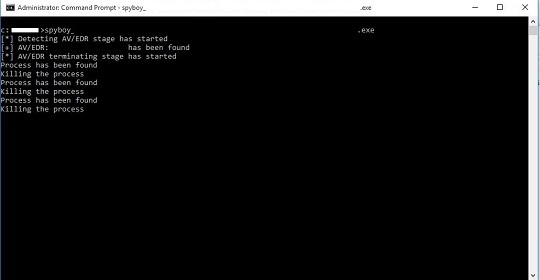
- It requires being executed with Administrative privileges to proceed with its routine.
SOLUTION
Step 1
Trend Micro Predictive Machine Learning detects and blocks malware at the first sign of its existence, before it executes on your system. When enabled, your Trend Micro product detects this malware under the following machine learning name:
-
Troj.Win32.TRX.XXPE50FFF069
Step 2
Before doing any scans, Windows 7, Windows 8, Windows 8.1, and Windows 10 users must disable System Restore to allow full scanning of their computers.
Step 3
Note that not all files, folders, and registry keys and entries are installed on your computer during this malware's/spyware's/grayware's execution. This may be due to incomplete installation or other operating system conditions. If you do not find the same files/folders/registry information, please proceed to the next step.
Step 4
Restart in Safe Mode
Step 5
Delete this registry value
Important: Editing the Windows Registry incorrectly can lead to irreversible system malfunction. Please do this step only if you know how or you can ask assistance from your system administrator. Else, check this Microsoft article first before modifying your computer's registry.
- In HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services
- {Random Driver Name} = \%System%\drivers\{Random Driver Name}.sys
- {Random Driver Name} = \%System%\drivers\{Random Driver Name}.sys
Step 6
Search and delete these files
- %System%\drivers\{Random Driver Name}.sys
Step 7
Restart in normal mode and scan your computer with your Trend Micro product for files detected as Trojan.Win64.SPYBOY.A. If the detected files have already been cleaned, deleted, or quarantined by your Trend Micro product, no further step is required. You may opt to simply delete the quarantined files. Please check this Knowledge Base page for more information.
Did this description help? Tell us how we did.