Trojan.Win32.APPLEJEUS.YEBB-A

Mal/BadCert-Gen (SOPHOS_LITE)
Windows




Threat Type: Trojan
Destructiveness: No
Encrypted:
In the wild: Yes
OVERVIEW
This Trojan arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites. It arrives as a component bundled with malware/grayware packages. It may be dropped by other malware.
As of this writing, the said sites are inaccessible.
TECHNICAL DETAILS
Arrival Details
This Trojan arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
It arrives as a component bundled with malware/grayware packages.
It may be dropped by the following malware:
- a Windows Microsoft Installer detected as Trojan.Win32.APPLEJEUS.YXBB-A
Installation
This Trojan drops the following non-malicious files:
- {Malware Directory}\CelasTraderPro.cfg
- saves default configuration for application
It creates the following folders:
- {Malware Directory}\CelasTradePro
- used by application to save configurations ang cache
Download Routine
This Trojan connects to the following URL(s) to download its configuration file:
- http://www.{BLOCKED}lc.com/api/GetFeaturedExchanges
- http://www.{BLOCKED}lc.com/resource/Currencies.ini
As of this writing, the said sites are inaccessible.
Other Details
This Trojan does the following:
- it is a modified version of QT Bitcoin Trader
- it displays a trojanized cryptocurrency trading platform named Celas Limited
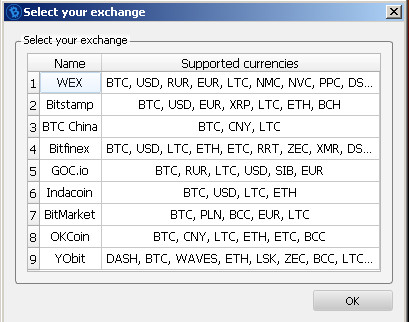
- no malicious behavior found during execution
SOLUTION
Step 1
Before doing any scans, Windows 7, Windows 8, Windows 8.1, and Windows 10 users must disable System Restore to allow full scanning of their computers.
Step 2
Note that not all files, folders, and registry keys and entries are installed on your computer during this malware's/spyware's/grayware's execution. This may be due to incomplete installation or other operating system conditions. If you do not find the same files/folders/registry information, please proceed to the next step.
Step 3
Remove the malware/grayware file dropped/downloaded by Trojan.Win32.APPLEJEUS.YEBB-A. (Note: Please skip this step if the threat(s) listed below have already been removed.)
- {Malware Directory}\CelasTraderPro.cfg
Step 4
Search and delete these folders
- {Malware Directory}\CelasTradePro
Step 5
Scan your computer with your Trend Micro product to delete files detected as Trojan.Win32.APPLEJEUS.YEBB-A. If the detected files have already been cleaned, deleted, or quarantined by your Trend Micro product, no further step is required. You may opt to simply delete the quarantined files. Please check the following Trend Micro Support pages for more information:
Did this description help? Tell us how we did.