TROJ_STRUPLOADER.ZYHD-A

Windows




Threat Type: Trojan
Destructiveness: No
Encrypted: Yes
In the wild: Yes
OVERVIEW
This Trojan arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
TECHNICAL DETAILS
Arrival Details
This Trojan arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
Other Details
This Trojan does the following:
- It requires the following parameters to perform its intended routine:
- {Web service} {Client ID} {Path of File where data will be retrieved}
- It sends data through POST request to the following URL:
client_id={Client ID}&scope=onedrive.readwrite+wl.offline_access+wl.signin&code={Client ID}&grant_type=authorization_code&redirect_uri=https://login.live.com/oauth20_desktop.srf
- If request is successful it will generate token and will use it to upload data. It displays the following message on console if token is generated:
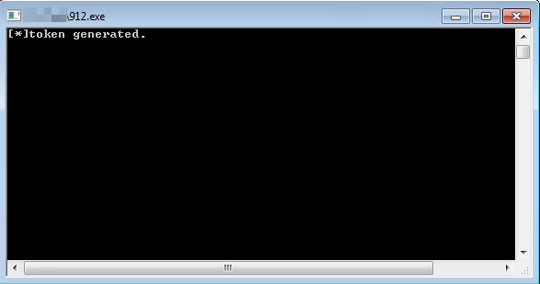
- If request is successful it will generate token and will use it to upload data. It displays the following message on console if token is generated:
SOLUTION
Step 1
Trend Micro Predictive Machine Learning detects and blocks malware at the first sign of its existence, before it executes on your system. When enabled, your Trend Micro product detects this malware under the following machine learning name:
- Troj.Win32.TRX.XXPE50FFF040
Step 2
Before doing any scans, Windows 7, Windows 8, Windows 8.1, and Windows 10 users must disable System Restore to allow full scanning of their computers.
Step 3
Scan your computer with your Trend Micro product to delete files detected as TROJ_STRUPLOADER.ZYHD-A. If the detected files have already been cleaned, deleted, or quarantined by your Trend Micro product, no further step is required. You may opt to simply delete the quarantined files. Please check the following Trend Micro Support pages for more information:
Did this description help? Tell us how we did.