Ransom.Win64.SORENA.A

W32/Sorena.AY!tr.ransom (FORTINET); Trojan-Ransom.FileCrypter (IKARUS)
Windows




Threat Type: Ransomware
Destructiveness: No
Encrypted: Yes
In the wild: Yes
OVERVIEW
This Ransomware arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
It drops files as ransom note. It avoids encrypting files with the following file extensions.
TECHNICAL DETAILS
Arrival Details
This Ransomware arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
Other System Modifications
This Ransomware deletes the following folders:
- AppData in all users (with allowed permissions for Everyone)
- {Drive letter}:\$Recycle.Bin
Process Termination
This Ransomware terminates the following processes if found running in the affected system's memory:
- sqlservr.exe
- sqlceip.exe
- sqlwriter.exe
Other Details
This Ransomware does the following:
- It avoids encrypting files with the following file names:
- Unlock_All_Files.txt
- Encrypt.exe
- ngrok.exe
Ransomware Routine
This Ransomware avoids encrypting files found in the following folders:
- C:\Windows
- C:\Program Files\VMWare
- C:\Program Files\Common Files
- C:\Program Files\Internet Explorer
- C:\Program Files\Reference Assemblies
- C:\Program Files (x86)\Reference Assemblies
- C:\Program Files (x86)\Common Files
- C:\Program Files (x86)\Internet Explorer
- C:\Program Files\WindowsApps
- C:\Program Files\Embedded Lockdown Manager
- C:\ProgramData\Microsoft
It appends the following extension to the file name of the encrypted files:
- .Email=[decryptfiles5@gmail.com]ID=[{unique ID}].encrypt
It drops the following file(s) as ransom note:
- %Desktop%\Unlock_All_Files.txt
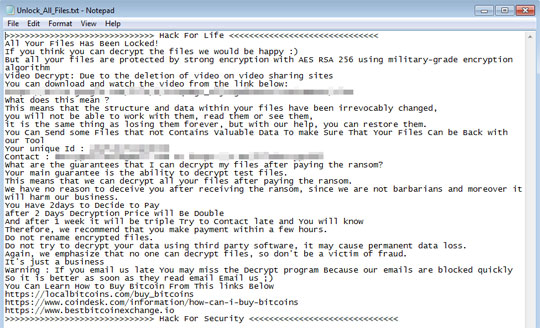
- %Application Data%\Microsoft\Windows\Network Shortcuts\Unlock_All_Files.txt
- %Public%\Desktop\Unlock_All_Files.txt
- %Public%\AppData\Roaming\Microsoft\Windows\Network Shortcuts\Unlock_All_Files.txt
- C:\Users\Default\Desktop\Unlock_All_Files.txt
- C:\Users\Default\AppData\Roaming\Microsoft\Windows\Network Shortcuts\Unlock_All_Files.txt
It avoids encrypting files with the following file extensions:
- .ini
- .log
- .resources
SOLUTION
Step 1
Before doing any scans, Windows 7, Windows 8, Windows 8.1, and Windows 10 users must disable System Restore to allow full scanning of their computers.
Step 2
Note that not all files, folders, and registry keys and entries are installed on your computer during this malware's/spyware's/grayware's execution. This may be due to incomplete installation or other operating system conditions. If you do not find the same files/folders/registry information, please proceed to the next step.
Step 3
Search and delete these files
- %Desktop%\Unlock_All_Files.txt
- %Application Data%\Microsoft\Windows\Network Shortcuts\Unlock_All_Files.txt
- %Public%\Desktop\Unlock_All_Files.txt
- %Public%\AppData\Roaming\Microsoft\Windows\Network Shortcuts\Unlock_All_Files.txt
- C:\Users\Default\Desktop\Unlock_All_Files.txt
- C:\Users\Default\AppData\Roaming\Microsoft\Windows\Network Shortcuts\Unlock_All_Files.txt
Step 4
Scan your computer with your Trend Micro product to delete files detected as Ransom.Win64.SORENA.A. If the detected files have already been cleaned, deleted, or quarantined by your Trend Micro product, no further step is required. You may opt to simply delete the quarantined files. Please check the following Trend Micro Support pages for more information:
Step 5
Restore encrypted files from backup.
Did this description help? Tell us how we did.