Ransom.Win32.AURORA.THCOCBA

Ransom:Win32/Aurora.PI (MICROSOFT); Trojan-Ransom.Win32.Cryptor.dsz (KASPERSKY)
Windows




Threat Type: Ransomware
Destructiveness: No
Encrypted: Yes
In the wild: Yes
OVERVIEW
This Ransomware arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
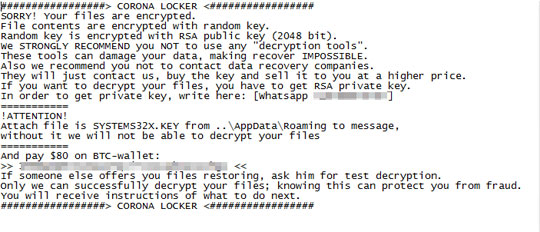
It encrypts files with specific file extensions. It drops files as ransom note.
TECHNICAL DETAILS
Arrival Details
This Ransomware arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
Installation
This Ransomware drops the following files:
- %Application Data%\SYSTEMS32X.KEY
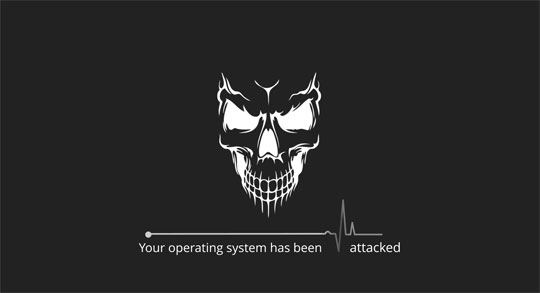
- {Malware Directory}\coronovi.rus → Used as wallpaper.
(Note: %Application Data% is the current user's Application Data folder, which is usually C:\Documents and Settings\{user name}\Application Data on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\AppData\Roaming on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).)
Autostart Technique
This Ransomware adds the following registry entries to enable its automatic execution at every system startup:
HKEY_CURRENT_USER\Software\Microsoft\
Windows\CurrentVersion\Run
MSFEEditor = {Malware Directory}\{Malware Filename}.exe e
Other System Modifications
This Ransomware changes the desktop wallpaper by modifying the following registry entries:
HKEY_CURRENT_USER\Control Panel\Desktop
Wallpaper = coronovi.rus
It sets the system's desktop wallpaper to the following image:
Other Details
This Ransomware does the following:
- If encryption is successful, it deletes itself using the following command:
- %System%\cmd.exe /c del {Malware Directory}\{Malware Filename}.exe e >> NUL
(Note: %System% is the Windows system folder, where it usually is C:\Windows\System32 on all Windows operating system versions.)
Ransomware Routine
This Ransomware encrypts files with the following extensions:
- 123
- 1c
- 1cd
- 3dm
- 3ds
- 3fr
- 3g2
- 3gp
- 3pr
- 602
- 7z
- 7zip
- _ms
- aac
- ab4
- abd
- accdb
- accde
- accdr
- accdt
- ace
- ach
- acr
- act
- adb
- adi
- adp
- ads
- aes
- afi
- agdl
- ai
- aiff
- aii
- air
- ais
- ait
- aiv
- al
- alg
- allet
- ams
- aocla
- aoi
- apj
- apk
- arc
- arch00
- arm
- art
- arw
- arz
- asc
- asf
- asm
- asp
- aspx
- asset
- asx
- avhdx
- avi
- awg
- backup
- backupdb
- bank
- bar
- bat
- bay
- bc6
- bc7
- bck
- bco
- bdb
- bgt
- big
- bik
- bin
- bkf
- bkp
- bkup
- blend
- blob
- bmp
- bpn
- bpw
- brd
- bsa
- bsm
- bxl
- bz2
- c
- cad
- cam
- cas
- cbk
- cbu
- cdf
- cdr
- cdr3
- cdr4
- cdr5
- cdr6
- cdrw
- cdx
- ce1
- ce2
- cel
- cer
- cert
- cf
- cfg
- cfr
- cgi
- cgm
- chg
- cib
- ckt
- class
- classpath
- cls
- cmd
- cmt
- cnf
- con
- config
- contact
- cpa
- cpi
- cpp
- cpr
- cr2
- craw
- crt
- crw
- cs
- csa
- csh
- cshtml
- csl
- csr
- css
- csv
- ctl
- cwz
- d
- d3dbsp
- dac
- das
- dat
- data
- dazip
- db0
- db3
- db5
- db_journal
- dba
- dbc
- dbf
- dbs
- dbx
- dc2
- dch
- dcr
- dcs
- ddb
- ddd
- ddoc
- ddrw
- dds
- der
- des
- desc
- design
- dft
- dgc
- dif
- dip
- dit
- djvu
- dmp
- dng
- doc
- docb
- docm
- docx
- dot
- dotm
- dotx
- dra
- drf
- drl
- dru
- drw
- dsn
- dsnwrk
- dt
- dtd
- dwg
- dxb
- dxf
- dxg
- e
- ecf
- edb
- edf
- elt
- eml
- emz
- epk
- eps
- erbsql
- erf
- esm
- ewprj
- exf
- fdb
- ff
- ffd
- fff
- fh
- fhd
- fla
- flac
- flf
- flp
- flv
- flvv
- fods
- fodt
- forge
- fos
- fp7
- fpd
- fpk
- fpx
- frm
- fsh
- fxg
- g1
- g2
- g3
- g4
- gbl
- gbo
- gbp
- gbr
- gbs
- gbx
- gdb
- gho
- gif
- gko
- gml
- gp
- gp1
- gp2
- gp3
- gp4
- gpb
- gpg
- gpt
- gray
- grb
- grey
- groups
- gry
- gtl
- gto
- gtp
- gts
- gwk
- gz
- h
- hbk
- hdd
- hkdb
- hkx
- hplg
- hpp
- html
- hvpl
- hwp
- ibank
- ibd
- ibz
- icxs
- idb
- idc
- idx
- iif
- iiq
- incpas
- indd
- info
- ip
- ipc
- ism
- iso
- itdb
- itl
- itm
- iwd
- iwi
- ix
- jar
- java
- jnt
- jpe
- jpeg
- jpg
- jrl
- js
- jsp
- kc2
- kdb
- kdbx
- kdc
- kf
- kicad
- kpdx
- kwm
- laccdb
- lay
- lay6
- layout
- lbf
- lbr
- lc
- lck
- ldb
- ldf
- lg
- lgc
- lia
- lib
- libprj
- license
- licz
- lit
- litemod
- llx
- lmc
- log
- lrf
- ltx
- lua
- lvl
- lyt
- lzh
- lzma
- m
- m2
- m2ts
- m3u
- m4a
- m4p
- m4u
- m4v
- map
- mapimail
- max
- mbx
- mcmeta
- md
- mdb
- mdbackup
- mdc
- mddata
- mdf
- mef
- menu
- mfw
- mid
- mkv
- mlb
- mlx
- mml
- mmw
- mny
- moneywell
- mos
- mov
- mp3
- mp4
- mpeg
- mpg
- mpqge
- mrg
- mrw
- mrwref
- msg
- mst
- mts
- myd
- myi
- mysql
- mysqli
- nbd
- nc
- ncf
- nd
- ndd
- ndf
- nef
- nk2
- nop
- nrw
- ns2
- ns3
- ns4
- nsd
- nsf
- nsg
- nsh
- ntl
- nvram
- nwb
- nx2
- nxl
- nyf
- oab
- obj
- obk
- odb
- odc
- odf
- odg
- odm
- odp
- ods
- odt
- oeb
- ogg
- oil
- olb
- one
- onetoc2
- opj
- opt
- ora
- orf
- ost
- otg
- oth
- otp
- ots
- ott
- p
- p12
- p7b
- p7c
- pab
- pad
- pages
- pak
- paq
- par
- pas
- pat
- pbd
- pc
- pcb
- pcbdoc
- pcd
- pct
- pdb
- pdblib
- pdd
- pef
- pem
- pfx
- phj
- phl
- pho
- php
- pif
- pkpass
- pl
- plc
- plus_muhd
- png
- pot
- potm
- potx
- ppam
- ppc
- pps
- ppsm
- ppsx
- ppt
- pptm
- pptx
- prf
- prj
- prjcor
- prjemb
- prjpcb
- pro
- project
- prt
- ps
- ps1
- psafe3
- psc
- psd
- psk
- psm
- pspimage
- pst
- ptx
- pwm
- py
- q99
- qb1
- qba
- qbb
- qbk
- qbm
- qbmb
- qbmd
- qbquery
- qbr
- qbw
- qbx
- qby
- qcow
- qcow2
- qdf
- qed
- qfd
- qfx
- qic
- qif
- qmd
- qry
- quicken
- quicken2015backup
- quicken2016backup
- quicken2017backup
- qw5
- r3d
- raf
- rar
- rat
- raw
- rb
- rdb
- re4
- reu
- rgss3a
- rim
- rm
- rofl
- rou
- rtf
- rul
- rvt
- rw2
- rwl
- rwz
- s3db
- safe
- sal
- sas7bdat
- sav
- save
- say
- sb
- sbn
- sbx
- sch
- schdoc
- schlib
- sd0
- sda
- sdf
- sh
- shp
- shx
- sid
- sidd
- sidn
- sie
- sis
- sl2
- sl3
- sldm
- sldx
- slk
- slm
- sln
- snt
- snx
- spp
- sqb
- sql
- sqlite
- sqlite3
- sqlitedb
- sqr
- sr2
- srf
- srt
- srw
- ssq
- st4
- st5
- st6
- st7
- st8
- stc
- std
- sti
- stm
- stp
- stw
- stx
- sum
- suo
- svg
- swf
- sxc
- sxd
- sxg
- sxi
- sxm
- sxw
- syncdb
- t12
- t13
- tar
- tax
- tbk
- tcf
- tex
- tga
- tgz
- thm
- tib
- tif
- tiff
- tlg
- tmd
- tmp
- tor
- trn
- txt
- ub
- uop
- uot
- upk
- vb
- vbk
- vbm
- vbox
- vbs
- vcd
- vcf
- vdf
- vdi
- vfs0
- vhd
- vhdx
- vib
- vlb
- vmdk
- vmem
- vmsd
- vmx
- vmxf
- vob
- vom
- vpk
- vpp_pc
- vsd
- vsdx
- vtf
- w3x
- wab
- wad
- wallet
- wav
- wb2
- wbk
- wdb
- wk1
- wks
- wma
- wmo
- wmv
- zip
- xml
- xls
- xlsx
It appends the following extension to the file name of the encrypted files:
- .systems32x
It drops the following file(s) as ransom note:
- {Encrypted Directory}\@_FILES_WERE_ENCRYPTED_@.TXT
- {Encrypted Directory}\@_HOW_TO_PAY_THE_RANSOM_@.TXT
- {Encrypted Directory}\@_HOW_TO_DECRYPT_FILES_@.TXT
SOLUTION
Step 1
Trend Micro Predictive Machine Learning detects and blocks malware at the first sign of its existence, before it executes on your system. When enabled, your Trend Micro product detects this malware under the following machine learning name:
- Troj.Win32.TRX.XXPE50FFF042
Step 2
Before doing any scans, Windows 7, Windows 8, Windows 8.1, and Windows 10 users must disable System Restore to allow full scanning of their computers.
Step 3
Note that not all files, folders, and registry keys and entries are installed on your computer during this malware's/spyware's/grayware's execution. This may be due to incomplete installation or other operating system conditions. If you do not find the same files/folders/registry information, please proceed to the next step.
Step 4
Delete this registry value
Important: Editing the Windows Registry incorrectly can lead to irreversible system malfunction. Please do this step only if you know how or you can ask assistance from your system administrator. Else, check this Microsoft article first before modifying your computer's registry.
- In HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
- MSFEEditor = {Malware Directory}\{Malware Filename}.exe e
- MSFEEditor = {Malware Directory}\{Malware Filename}.exe e
Step 5
Search and delete this file
- %Application Data%\SYSTEMS32X.KEY
- {Malware Directory}\coronovi.rus
- {Encrypted Directory}\@_FILES_WERE_ENCRYPTED_@.TXT
- {Encrypted Directory}\@_HOW_TO_PAY_THE_RANSOM_@.TXT
- {Encrypted Directory}\@_HOW_TO_DECRYPT_FILES_@.TXT
Step 6
Reset your Desktop properties
Step 7
Scan your computer with your Trend Micro product to delete files detected as Ransom.Win32.AURORA.THCOCBA. If the detected files have already been cleaned, deleted, or quarantined by your Trend Micro product, no further step is required. You may opt to simply delete the quarantined files. Please check the following Trend Micro Support pages for more information:
Step 8
Restore encrypted files from backup.
Did this description help? Tell us how we did.