PUA.Win64.PCAppStore.C

Windows




Threat Type: Potentially Unwanted Application
Destructiveness: No
Encrypted:
In the wild: Yes
OVERVIEW
This Potentially Unwanted Application arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
It does not have any propagation routine.
It does not have any backdoor routine.
It connects to certain websites to send and receive information.
TECHNICAL DETAILS
Arrival Details
This Potentially Unwanted Application arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
Installation
This Potentially Unwanted Application drops the following files:
- %User Temp%\ns{Random 5 characters}.tmp\System.dll → Deleted Afterwards
- %User Temp%\ns{Random 5 characters}.tmp\UAC.dll → Deleted Afterwards
- %User Temp%\ns{Random 5 characters}.tmp\NSISFastLib.dll → Deleted Afterwards
- %User Temp%\ns{Random 5 characters}.tmp\nsJSON.dll → Deleted Afterwards
- %User Temp%\ns{Random 5 characters}.tmp\Math.dll → Deleted Afterwards
- %User Temp%\ns{Random 5 characters}.tmp\inetc.dll → Deleted Afterwards
- %User Temp%\temp
- %User Temp%\ns{Random 5 characters}.tmp\nsDialogs.dll → Deleted Afterwards
- %User Temp%\ns{Random 5 characters}.tmp\wimage.bmp → Deleted Afterwards
- %User Temp%\ns{Random 5 characters}.tmp\SimpleSC.dll → Deleted Afterwards
- %Program Files%\PCAppStore\ReadMe.txt
- %Program Files%\PCAppStore\pcappstore.ico
- %User Temp%\ns{Random 5 characters}.tmp\Watchdog.exe → Deleted Afterwards
- %Program Files%\PCAppStore\Watchdog.exe
- %User Temp%\ns{Random 5 characters}.tmp\PCAppStore.exe → Deleted Afterwards
- %Program Files%\PCAppStore\PCAppStore.exe
- %User Temp%\ns{Random 5 characters}.tmp\AutoUpdater.exe → Deleted Afterwards
- %Program Files%\PCAppStore\AutoUpdater.exe
- %User Temp%\ns{Random 5 characters}.tmp\PCAppStoreSRV.exe → Deleted Afterwards
- %Program Files%\PCAppStore\PcAppStoreSRV.exe
- %Program Files%\PCAppStore\Uninstaller.exe
- %Programs%\PC App Store.lnk
- %Desktop%\PC App Store.lnk
- %Common Programs%\PC App Store.lnk
(Note: %User Temp% is the current user's Temp folder, which is usually C:\Documents and Settings\{user name}\Local Settings\Temp on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\AppData\Local\Temp on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).. %Program Files% is the default Program Files folder, usually C:\Program Files in Windows 2000(32-bit), Server 2003(32-bit), XP, Vista(64-bit), 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit) , or C:\Program Files (x86) in Windows XP(64-bit), Vista(64-bit), 7(64-bit), 8(64-bit), 8.1(64-bit), 2008(64-bit), 2012(64-bit) and 10(64-bit).. %Programs% is the folder that contains the user’s program groups, which is usually C:\Windows\Start Menu\Programs or C:\Documents and Settings\{User name}\Start Menu\Programs on Windows 2000, XP, and Server 2003, or C:\Users\{user name}\AppData\Roaming\Microsoft\Windows\Start Menu\Programs on Windows Vista, 7, and 8.. %Desktop% is the current user's desktop, which is usually C:\Documents and Settings\{User Name}\Desktop on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\Desktop on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).. %Common Programs% is the folder that contains common program groups for all users, which is usually C:\Documents and Settings\All Users\Start Menu\Programs on Windows 2000, XP, and Server 2003, or C:\ProgramData\Microsoft\Windows\Start Menu\Programs on Windows Vista, 7, and 8.)
Other System Modifications
This Potentially Unwanted Application adds the following registry entries:
HKEY_LOCAL_MACHINE\SOFTWARE\PCAppStore
InstallPath = %Program Files%\PCAppStore
HKEY_CURRENT_USER\Software\PCAppStore
status = 0
HKEY_CURRENT_USER\Software\PCAppStore
IsRoot = 1
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\CurrentVersion\Uninstall\
PCAppStore
DisplayName = PC App Store
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\CurrentVersion\Uninstall\
PCAppStore
UninstallString = "%Program Files%\PCAppStore\Uninstaller.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\CurrentVersion\Uninstall\
PCAppStore
DisplayIcon = "%Program Files%\PCAppStore\Uninstaller.exe"
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\CurrentVersion\Uninstall\
PCAppStore
Publisher = Fast Corporation LTD
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\CurrentVersion\Uninstall\
PCAppStore
DisplayVersion = fa.2024
HKEY_LOCAL_MACHINE\SOFTWARE\Classes\
PcAppStore
URL:PC App Store =
HKEY_LOCAL_MACHINE\SOFTWARE\Classes\
PcAppStore
URL Protocol = pcappstore
HKEY_LOCAL_MACHINE\SOFTWARE\Classes\
PcAppStore
DefaultIcon = %Program Files%\PCAppStore\PCAppStore.exe,1
HKEY_LOCAL_MACHINE\SOFTWARE\Classes\
PcAppStore\shell\open\
command
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
AutoUpdater.exe
DumpCount = 20
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
AutoUpdater.exe
DumpFolder = %Program Files%\PCAppStore\Errors
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
AutoUpdater.exe
DumpType = 1
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
PCAppStore.exe
DumpCount = 20
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
PCAppStore.exe
DumpFolder = %Program Files%\PCAppStore\Errors
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
PCAppStore.exe
DumpType = 1
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
PcAppStoreSRV.exe
DumpCount = 20
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
PcAppStoreSRV.exe
DumpFolder = %Program Files%\PCAppStore\Errors
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
PcAppStoreSRV.exe
DumpType = 1
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
Watchdog.exe
DumpCount = 20
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
Watchdog.exe
DumpFolder = %Program Files%\PCAppStore\Errors
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
Watchdog.exe
DumpType = 1
Propagation
This Potentially Unwanted Application does not have any propagation routine.
Backdoor Routine
This Potentially Unwanted Application does not have any backdoor routine.
Rootkit Capabilities
This Potentially Unwanted Application does not have rootkit capabilities.
Information Theft
This Potentially Unwanted Application gathers the following data:
- Machine GUID
- MAC Address
Other Details
This Potentially Unwanted Application adds the following registry keys:
HKEY_LOCAL_MACHINE\SOFTWARE\PCAppStore
HKEY_CURRENT_USER\Software\PCAppStore
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\CurrentVersion\Uninstall\
PCAppStore
HKEY_LOCAL_MACHINE\SOFTWARE\Classes\
PcAppStore
HKEY_LOCAL_MACHINE\SOFTWARE\Classes\
PcAppStore\shell
HKEY_LOCAL_MACHINE\SOFTWARE\Classes\
PcAppStore\shell\open
HKEY_LOCAL_MACHINE\SOFTWARE\Classes\
PcAppStore\shell\open\
command
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
AutoUpdater.exe
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
PCAppStore.exe
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
PcAppStoreSRV.exe
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\
Windows\Windows Error Reporting\LocalDumps\
Watchdog.exe
It connects to the following website to send and receive information:
- http://{BLOCKED}.store:443
- https://{BLOCKED}.store/pixel.gif?guid={ GUID}&version=fa.2024&evt_src=fa_g_installer&evt_action=localmac&addon[]={MAC Address}
It does the following:
- It creates a service with the following details:
- Name: PcAppStoreSRV
- Display Name: PcAppStore Service
- Type: Own Process
- Start type: Auto Start
- Binary Path: %Program Files%\PCAppStore\PcAppStoreSRV.exe
- It displays the following during installation:
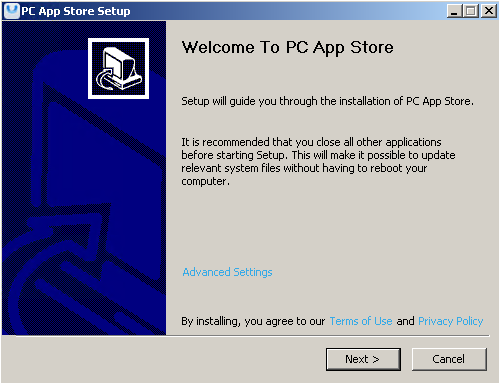
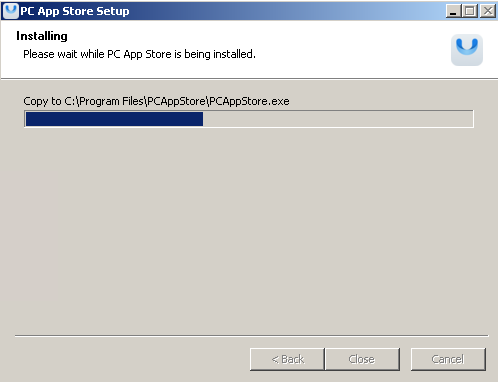
It does not exploit any vulnerability.
SOLUTION
Step 1
Before doing any scans, Windows 7, Windows 8, Windows 8.1, and Windows 10 users must disable System Restore to allow full scanning of their computers.
Step 2
Note that not all files, folders, and registry keys and entries are installed on your computer during this malware's/spyware's/grayware's execution. This may be due to incomplete installation or other operating system conditions. If you do not find the same files/folders/registry information, please proceed to the next step.
Step 3
Delete this registry key
Important: Editing the Windows Registry incorrectly can lead to irreversible system malfunction. Please do this step only if you know how or you can ask assistance from your system administrator. Else, check this Microsoft article first before modifying your computer's registry.
- In HKEY_LOCAL_MACHINE\SOFTWARE\PCAppStore
- In HKEY_CURRENT_USER\Software\PCAppStore
- In HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\PCAppStore
- In HKEY_LOCAL_MACHINE\SOFTWARE\Classes\PcAppStore
- In HKEY_LOCAL_MACHINE\SOFTWARE\Classes\PcAppStore\shell
- In HKEY_LOCAL_MACHINE\SOFTWARE\Classes\PcAppStore\shell\open
- In HKEY_LOCAL_MACHINE\SOFTWARE\Classes\PcAppStore\shell\open\command
- In HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps
- In HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\AutoUpdater.exe
- In HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\PCAppStore.exe
- In HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\PcAppStoreSRV.exe
- In HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\Watchdog.exe
Step 4
Delete this registry value
Important: Editing the Windows Registry incorrectly can lead to irreversible system malfunction. Please do this step only if you know how or you can ask assistance from your system administrator. Else, check this Microsoft article first before modifying your computer's registry.
- HKEY_LOCAL_MACHINE\SOFTWARE\PCAppStore
- InstallPath = %Program Files%\PCAppStore
- HKEY_CURRENT_USER\Software\PCAppStore
- status = 0
- HKEY_CURRENT_USER\Software\PCAppStore
- IsRoot = 1
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\PCAppStore
- DisplayName = PC App Store
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\PCAppStore
- UninstallString = "%Program Files%\PCAppStore\Uninstaller.exe"
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\PCAppStore
- DisplayIcon = "%Program Files%\PCAppStore\Uninstaller.exe"
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\PCAppStore
- Publisher = Fast Corporation LTD
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\PCAppStore
- DisplayVersion = fa.2024
- HKEY_LOCAL_MACHINE\SOFTWARE\Classes\PcAppStore
- = URL:PC App Store
- HKEY_LOCAL_MACHINE\SOFTWARE\Classes\PcAppStore
- URL Protocol = pcappstore
- HKEY_LOCAL_MACHINE\SOFTWARE\Classes\PcAppStore
- DefaultIcon = %Program Files%\PCAppStore\PCAppStore.exe,1
- HKEY_LOCAL_MACHINE\SOFTWARE\Classes\PcAppStore\shell\open\command
- [empty] = "%Program Files%\PCAppStore\PCAppStore.exe" /src=custom_protocol /query="%1"
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\AutoUpdater.exe
- DumpCount = 20
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\AutoUpdater.exe
- DumpFolder = %Program Files%\PCAppStore\Errors
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\AutoUpdater.exe
- DumpType = 1
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\PCAppStore.exe
- DumpCount = 20
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\PCAppStore.exe
- DumpFolder = %Program Files%\PCAppStore\Errors
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\PCAppStore.exe
- DumpType = 1
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\PcAppStoreSRV.exe
- DumpCount = 20
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\PcAppStoreSRV.exe
- DumpFolder = %Program Files%\PCAppStore\Errors
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\PcAppStoreSRV.exe
- DumpType = 1
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\Watchdog.exe
- DumpCount = 20
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\Watchdog.exe
- DumpFolder = %Program Files%\PCAppStore\Errors
- HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Windows Error Reporting\LocalDumps\Watchdog.exe
- DumpType = 1
Step 5
Search and delete this file
- %User Temp%\ns{Random 5 characters}.tmp\System.dll
- %User Temp%\ns{Random 5 characters}.tmp\UAC.dll
- %User Temp%\ns{Random 5 characters}.tmp\NSISFastLib.dll
- %User Temp%\ns{Random 5 characters}.tmp\nsJSON.dll
- %User Temp%\ns{Random 5 characters}.tmp\Math.dll
- %User Temp%\ns{Random 5 characters}.tmp\inetc.dll
- %User Temp%\temp
- %User Temp%\ns{Random 5 characters}.tmp\nsDialogs.dll
- %User Temp%\ns{Random 5 characters}.tmp\wimage.bmp
- %User Temp%\ns{Random 5 characters}.tmp\SimpleSC.dll
- %Program Files%\PCAppStore\ReadMe.txt
- %Program Files%\PCAppStore\pcappstore.ico
- %User Temp%\ns{Random 5 characters}.tmp\Watchdog.exe
- %Program Files%\PCAppStore\Watchdog.exe
- %User Temp%\ns{Random 5 characters}.tmp\PCAppStore.exe
- %Program Files%\PCAppStore\PCAppStore.exe
- %User Temp%\ns{Random 5 characters}.tmp\AutoUpdater.exe
- %Program Files%\PCAppStore\AutoUpdater.exe
- %User Temp%\ns{Random 5 characters}.tmp\PCAppStoreSRV.exe
- %Program Files%\PCAppStore\PcAppStoreSRV.exe
- %Program Files%\PCAppStore\Uninstaller.exe
- %Programs%\PC App Store.lnk
- %Desktop%\PC App Store.lnk
- %Common Programs%\PC App Store.lnk
Step 6
Scan your computer with your Trend Micro product to delete files detected as PUA.Win64.PCAppStore.C. If the detected files have already been cleaned, deleted, or quarantined by your Trend Micro product, no further step is required. You may opt to simply delete the quarantined files. Please check the following Trend Micro Support pages for more information:
Did this description help? Tell us how we did.