PUA.Win64.KeyGen.CRRM

a variant of Win64/HackTool.WinActivator.B potentially unsafe application (NOD32)
Windows



Threat Type: Hacking Tool
Destructiveness: No
Encrypted: No
In the wild: Yes
OVERVIEW
This Hacking Tool arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
It does not have any propagation routine.
It does not have any backdoor routine.
It does not have any information-stealing capability.
It connects to certain websites to send and receive information. It gathers information and reports it to its servers.
TECHNICAL DETAILS
Arrival Details
This Hacking Tool arrives on a system as a file dropped by other malware or as a file downloaded unknowingly by users when visiting malicious sites.
Installation
This Hacking Tool drops the following files:
- %User Temp%\test.dat → detected as HackTool.Win32.AutoKMS.AUSZP
(Note: %User Temp% is the current user's Temp folder, which is usually C:\Documents and Settings\{user name}\Local Settings\Temp on Windows 2000(32-bit), XP, and Server 2003(32-bit), or C:\Users\{user name}\AppData\Local\Temp on Windows Vista, 7, 8, 8.1, 2008(64-bit), 2012(64-bit) and 10(64-bit).)
It adds the following processes:
- "%System%\cmd.exe" /c Netsh.exe Advfirewall Firewall delete rule name=AAct_Network protocol=TCP
- "%System%\cmd.exe" /c Netsh.exe Advfirewall Firewall delete rule name=0pen_Port_KMS protocol=TCP
- "%System%\cmd.exe" /c Netsh.exe Advfirewall Firewall add rule name=AAct_Network dir=in action=allow protocol=TCP program="{Malware Path}\{Malware Filename}"
- "%System%\cmd.exe" /c Netsh.exe Advfirewall Firewall add rule name=AAct_Network dir=out action=allow protocol=TCP program="{Malware Path}\{Malware Filename}"
- "%System%\cmd.exe" /c Netsh.exe Advfirewall Firewall add rule name=0pen_Port_KMS dir=in action=allow protocol=TCP localport=1688
- "%System%\cmd.exe" /c %User Temp%\test.dat {BLOCKED}iboy.ir:1688 -l Windows -6
- "%System%\cmd.exe" /c %User Temp%\test.dat {BLOCKED}nancce.com:1688 -l Windows -6
- "%System%\cmd.exe" /c %User Temp%\test.dat {BLOCKED}322.org:1688 -l Windows -6
- "%System%\cmd.exe" /c %User Temp%\test.dat {BLOCKED}ro.cc:1688 -l Windows -6
- "%System%\cmd.exe" /c %User Temp%\test.dat {BLOCKED}9.com:1688 -l Windows -6
- "%System%\cmd.exe" /c %User Temp%\test.dat {BLOCKED}.crsoo.com:1688 -l Windows -6
- "%System%\cmd.exe" /c %User Temp%\test.dat {BLOCKED}k.org:1688 -l Windows -6
- "%System%\cmd.exe" /c %User Temp%\test.dat {BLOCKED}.{BLOCKED}.{BLOCKED}.170:1688 -l Windows -6
- If WINDOWS ACTIVATION button is clicked:
- "%System%\cmd.exe" /c cscript.exe %System%\slmgr.vbs //NoLogo /sdns
- "%System%\cmd.exe" /c cscript.exe %System%\slmgr.vbs //NoLogo /act-type 0
- "%System%\cmd.exe" /c cscript.exe %System%\slmgr.vbs //NoLogo /ckms
- "%System%\cmd.exe" /c cscript.exe %System%\slmgr.vbs //NoLogo /ckms-domain
- If OFFICE ACTIVATION/INFORMATION/PRODUCT KEY UNINSTALLATION button is clicked:
- "%System%\cmd.exe" /c REG QUERY HKLM\Software\Microsoft\Office /s /v Path /reg:64
- "%System%\cmd.exe" /c REG QUERY HKLM\Software\WOW6432Node\Microsoft\Office /s /v Path
- If WINDOWS INFORMATION button is clicked:
- "%System%\cmd.exe" /c cscript.exe %System%\slmgr.vbs //NoLogo /dli
- If INSTALL WINDOWS GVLK/OWN KEY button is clicked:
- "%System%\cmd.exe" /c cscript.exe %System%\slmgr.vbs //NoLogo /dlv All
- "%System%\cmd.exe" /c cscript.exe %System%\slmgr.vbs //NoLogo /ipk {Product Key}
- If UNINSTALL WINDOWS PRODUCT KEY button is clicked:
- "%System%\cmd.exe" /c cscript.exe %System%\slmgr.vbs //NoLogo /upk
Other System Modifications
This Hacking Tool adds the following registry entries:
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender
DisableAntiSpyware = 1
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender
AllowFastServiceStartup = 0
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender
ServiceKeepAlive = 0
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender\Real-Time Protection
DisableOnAccessProtection = 1
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender\Real-Time Protection
DisableBehaviorMonitoring = 1
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender\Real-Time Protection
DisableScanOnRealtimeEnable = 1
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender\Real-Time Protection
DisableIOAVProtection = 1
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender\Real-Time Protection
DisableRealtimeMonitoring = 1
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender\Spynet
DisableBlockAtFirstSeen = 1
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender\Spynet
LocalSettingOverrideSpynetReporting = 0
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender\Spynet
SubmitSamplesConsent = 2
Propagation
This Hacking Tool does not have any propagation routine.
Backdoor Routine
This Hacking Tool does not have any backdoor routine.
Rootkit Capabilities
This Hacking Tool does not have rootkit capabilities.
Information Theft
This Hacking Tool does not have any information-stealing capability.
Other Details
This Hacking Tool adds the following registry keys:
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender\Real-Time Protection
If DISABLE WINDOWS DEFENDER is checked:
HKEY_LOCAL_MACHINE\SOFTWARE\Policies\
Microsoft\Windows Defender\Spynet
It connects to the following website to send and receive information:
- KMS activation servers:
- {BLOCKED}iboy.ir:1688
- {BLOCKED}nancce.com:1688
- {BLOCKED}322.org:1688
- {BLOCKED}ro.cc:1688
- {BLOCKED}9.com:1688
- {BLOCKED}.crsoo.com:1688
- {BLOCKED}k.org:1688
- {BLOCKED}.{BLOCKED}.{BLOCKED}.170:1688
- If link to author information is clicked:
- https://{BLOCKED}l/M2ThD0
which redirects to:- https://{BLOCKED}u-board.com/topic.cgi?forum=2&topic=5559#1
- https://{BLOCKED}l/M2ThD0
It does the following:
- It uses the following keygen application:
- AAct Network x64 v1.1.5 Portable
- It displays the following GUI:
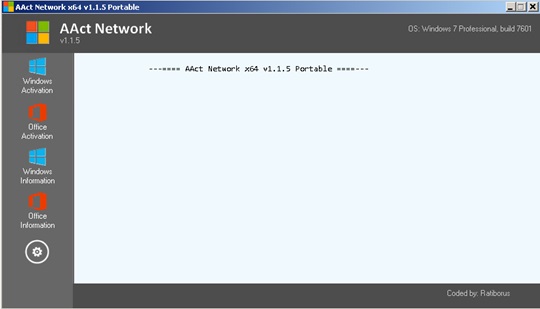
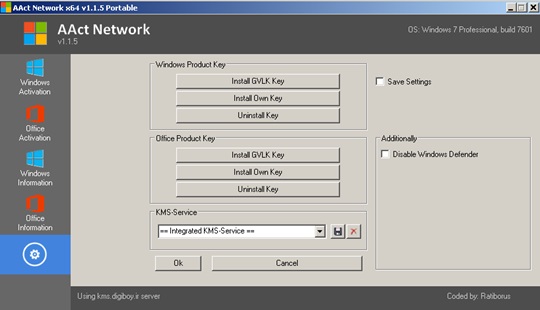
It gathers the following information and reports it to its servers:
- OS information and activation status
- Microsoft Office information and activation status
It does not exploit any vulnerability.
NOTES:
It does not exploit any vulnerability.
SOLUTION
Step 1
Before doing any scans, Windows 7, Windows 8, Windows 8.1, and Windows 10 users must disable System Restore to allow full scanning of their computers.
Step 2
Note that not all files, folders, and registry keys and entries are installed on your computer during this malware's/spyware's/grayware's execution. This may be due to incomplete installation or other operating system conditions. If you do not find the same files/folders/registry information, please proceed to the next step.
Step 3
Delete this registry value
Important: Editing the Windows Registry incorrectly can lead to irreversible system malfunction. Please do this step only if you know how or you can ask assistance from your system administrator. Else, check this Microsoft article first before modifying your computer's registry.
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender
- DisableAntiSpyware = 1
- DisableAntiSpyware = 1
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender
- AllowFastServiceStartup = 0
- AllowFastServiceStartup = 0
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender
- ServiceKeepAlive = 0
- ServiceKeepAlive = 0
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender\Real-Time Protection
- DisableOnAccessProtection = 1
- DisableOnAccessProtection = 1
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender\Real-Time Protection
- DisableBehaviorMonitoring = 1
- DisableBehaviorMonitoring = 1
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender\Real-Time Protection
- DisableScanOnRealtimeEnable = 1
- DisableScanOnRealtimeEnable = 1
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender\Real-Time Protection
- DisableIOAVProtection = 1
- DisableIOAVProtection = 1
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender\Real-Time Protection
- DisableRealtimeMonitoring = 1
- DisableRealtimeMonitoring = 1
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender\Spynet
- DisableBlockAtFirstSeen = 1
- DisableBlockAtFirstSeen = 1
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender\Spynet
- LocalSettingOverrideSpynetReporting = 0
- LocalSettingOverrideSpynetReporting = 0
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender\Spynet
- SubmitSamplesConsent = 2
- SubmitSamplesConsent = 2
Step 4
Delete this registry key
Important: Editing the Windows Registry incorrectly can lead to irreversible system malfunction. Please do this step only if you know how or you can ask assistance from your system administrator. Else, check this Microsoft article first before modifying your computer's registry.
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender\
- Real-Time Protection
- Real-Time Protection
- In HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Microsoft\Windows Defender\
- Spynet
- Spynet
Step 5
Search and delete this file
- %User Temp%\test.dat
Step 6
Scan your computer with your Trend Micro product to delete files detected as PUA.Win64.KeyGen.CRRM. If the detected files have already been cleaned, deleted, or quarantined by your Trend Micro product, no further step is required. You may opt to simply delete the quarantined files. Please check the following Trend Micro Support pages for more information:
Did this description help? Tell us how we did.